Navigation
Vault access. Public access is not open. This product is separate from initial Identity and Apparatus access.
Screenshots use fictional demonstration accounts. Your data and available actions may differ. Reviewed October 16, 2026.
Clients
Use the TypeScript client
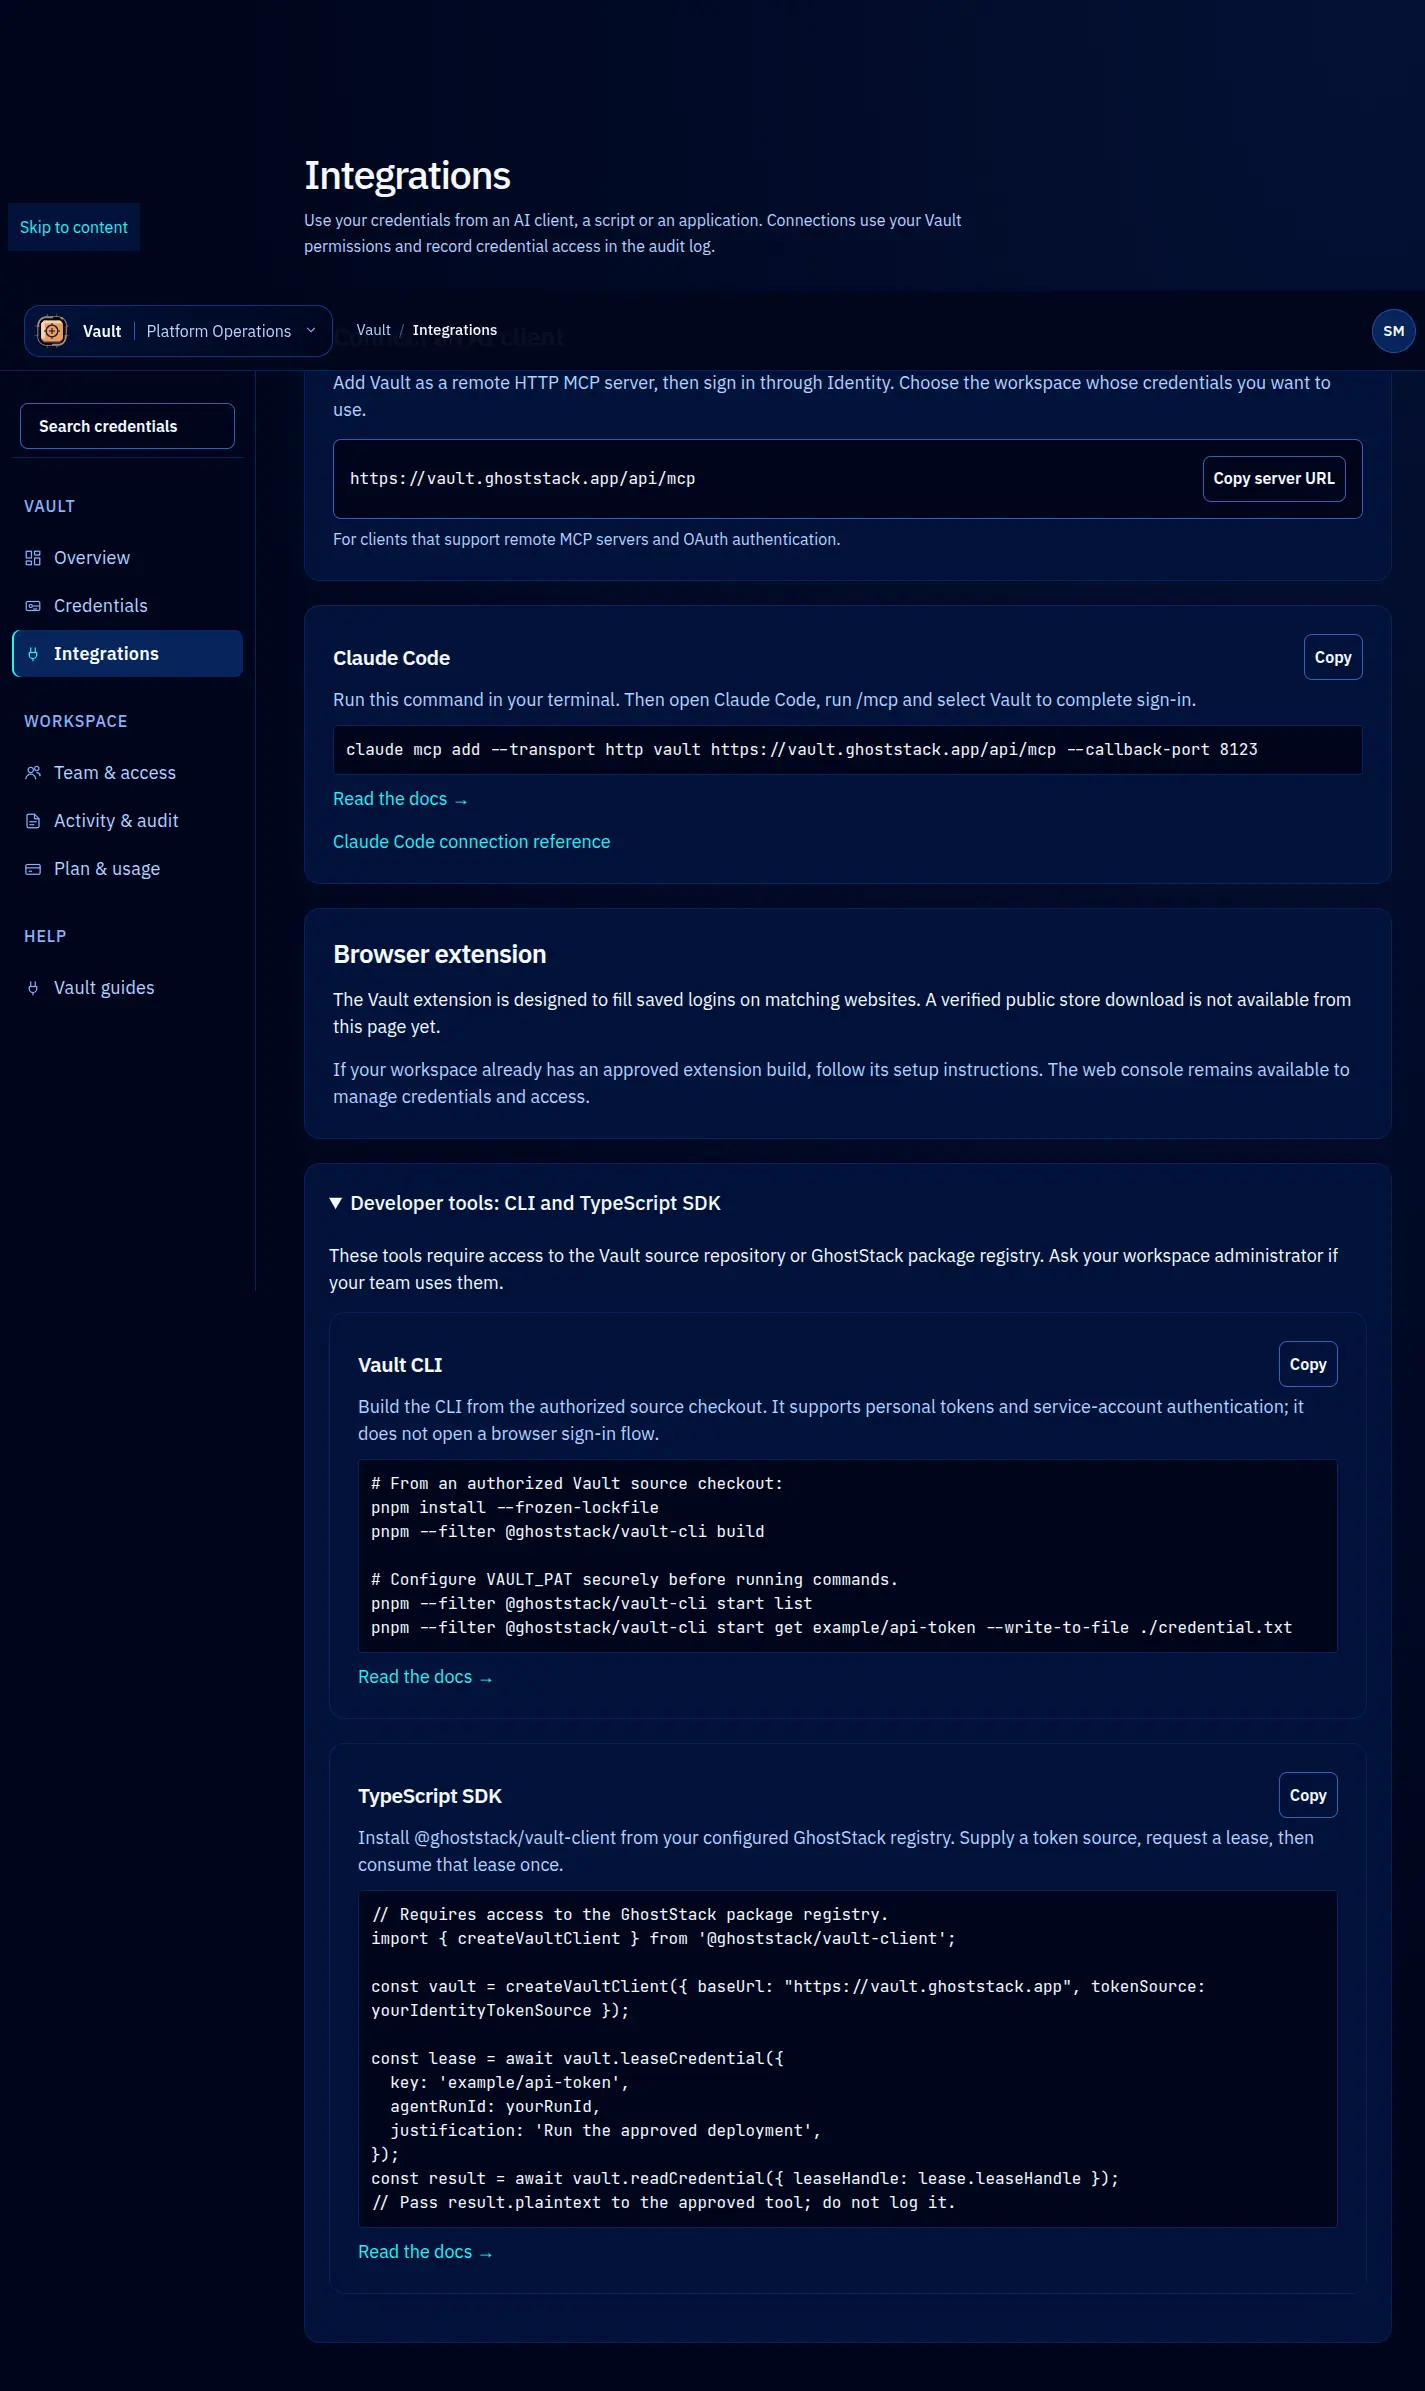
Use @ghoststack/vault-client from the private Rosecraft GitLab registry. Your operator must provide registry access and a valid Identity token source for the Vault REST audience. The package does not perform browser sign-in for you.
Create a client and lease a value
import { createVaultClient } from '@ghoststack/vault-client';

const vault = createVaultClient({
  baseUrl: 'https://vault.ghoststack.app',
  tokenSource: yourIdentityTokenSource,
});

const lease = await vault.leaseCredential({
  key: 'example/api-token',
  agentRunId: yourRunId,
  justification: 'Use the credential for the approved deployment',
});
const result = await vault.readCredential({
  leaseHandle: lease.leaseHandle,
});
// Pass result.plaintext only to the intended consumer. Do not log it.
yourIdentityTokenSource and yourRunId are application-provided values, not package exports. The token callback runs per request, allowing your application to refresh authorization. Use one valid run identifier for related work. The lease response includes its ID, handle and expiry; redemption consumes the handle.
Retrieve a structured record
For a typed credential, result.plaintext contains a JSON envelope with v, type and the type’s fields. Parse it and validate the expected type before using a field. A legacy untyped credential can instead contain a raw string.
| Record type | Primary field | Additional encrypted fields |
|---|---|---|
| Login | password | username, optional totpBackupCodes, service details |
| AWS access key | secretAccessKey | accessKeyId, region, optional sessionToken and profile |
| TLS bundle | privateKey | certificateChain and optional caBundle |
| Database | password | driver, host, port, database and user |
| Service-account JSON | json | provider and extracted account context |
The console’s Copy action returns only the labelled primary value. This client path retrieves the full encrypted record through the same authorized lease lifecycle. Keep auxiliary fields out of logs too.
Handle failures
Catch VaultClientError and inspect status and code. Authentication, scope denial, missing records, consumed handles and expiry require different recovery. Do not blindly retry a read with a consumed handle. Request a new lease only if the operation is still approved and necessary.
See the method reference for available operations and lease behavior for timing limits.
Screen reference