Navigation
Vault access. Public access is not open. This product is separate from initial Identity and Apparatus access.
Screenshots use fictional demonstration accounts. Your data and available actions may differ. Reviewed October 16, 2026.
Credential types
Store an AWS access key
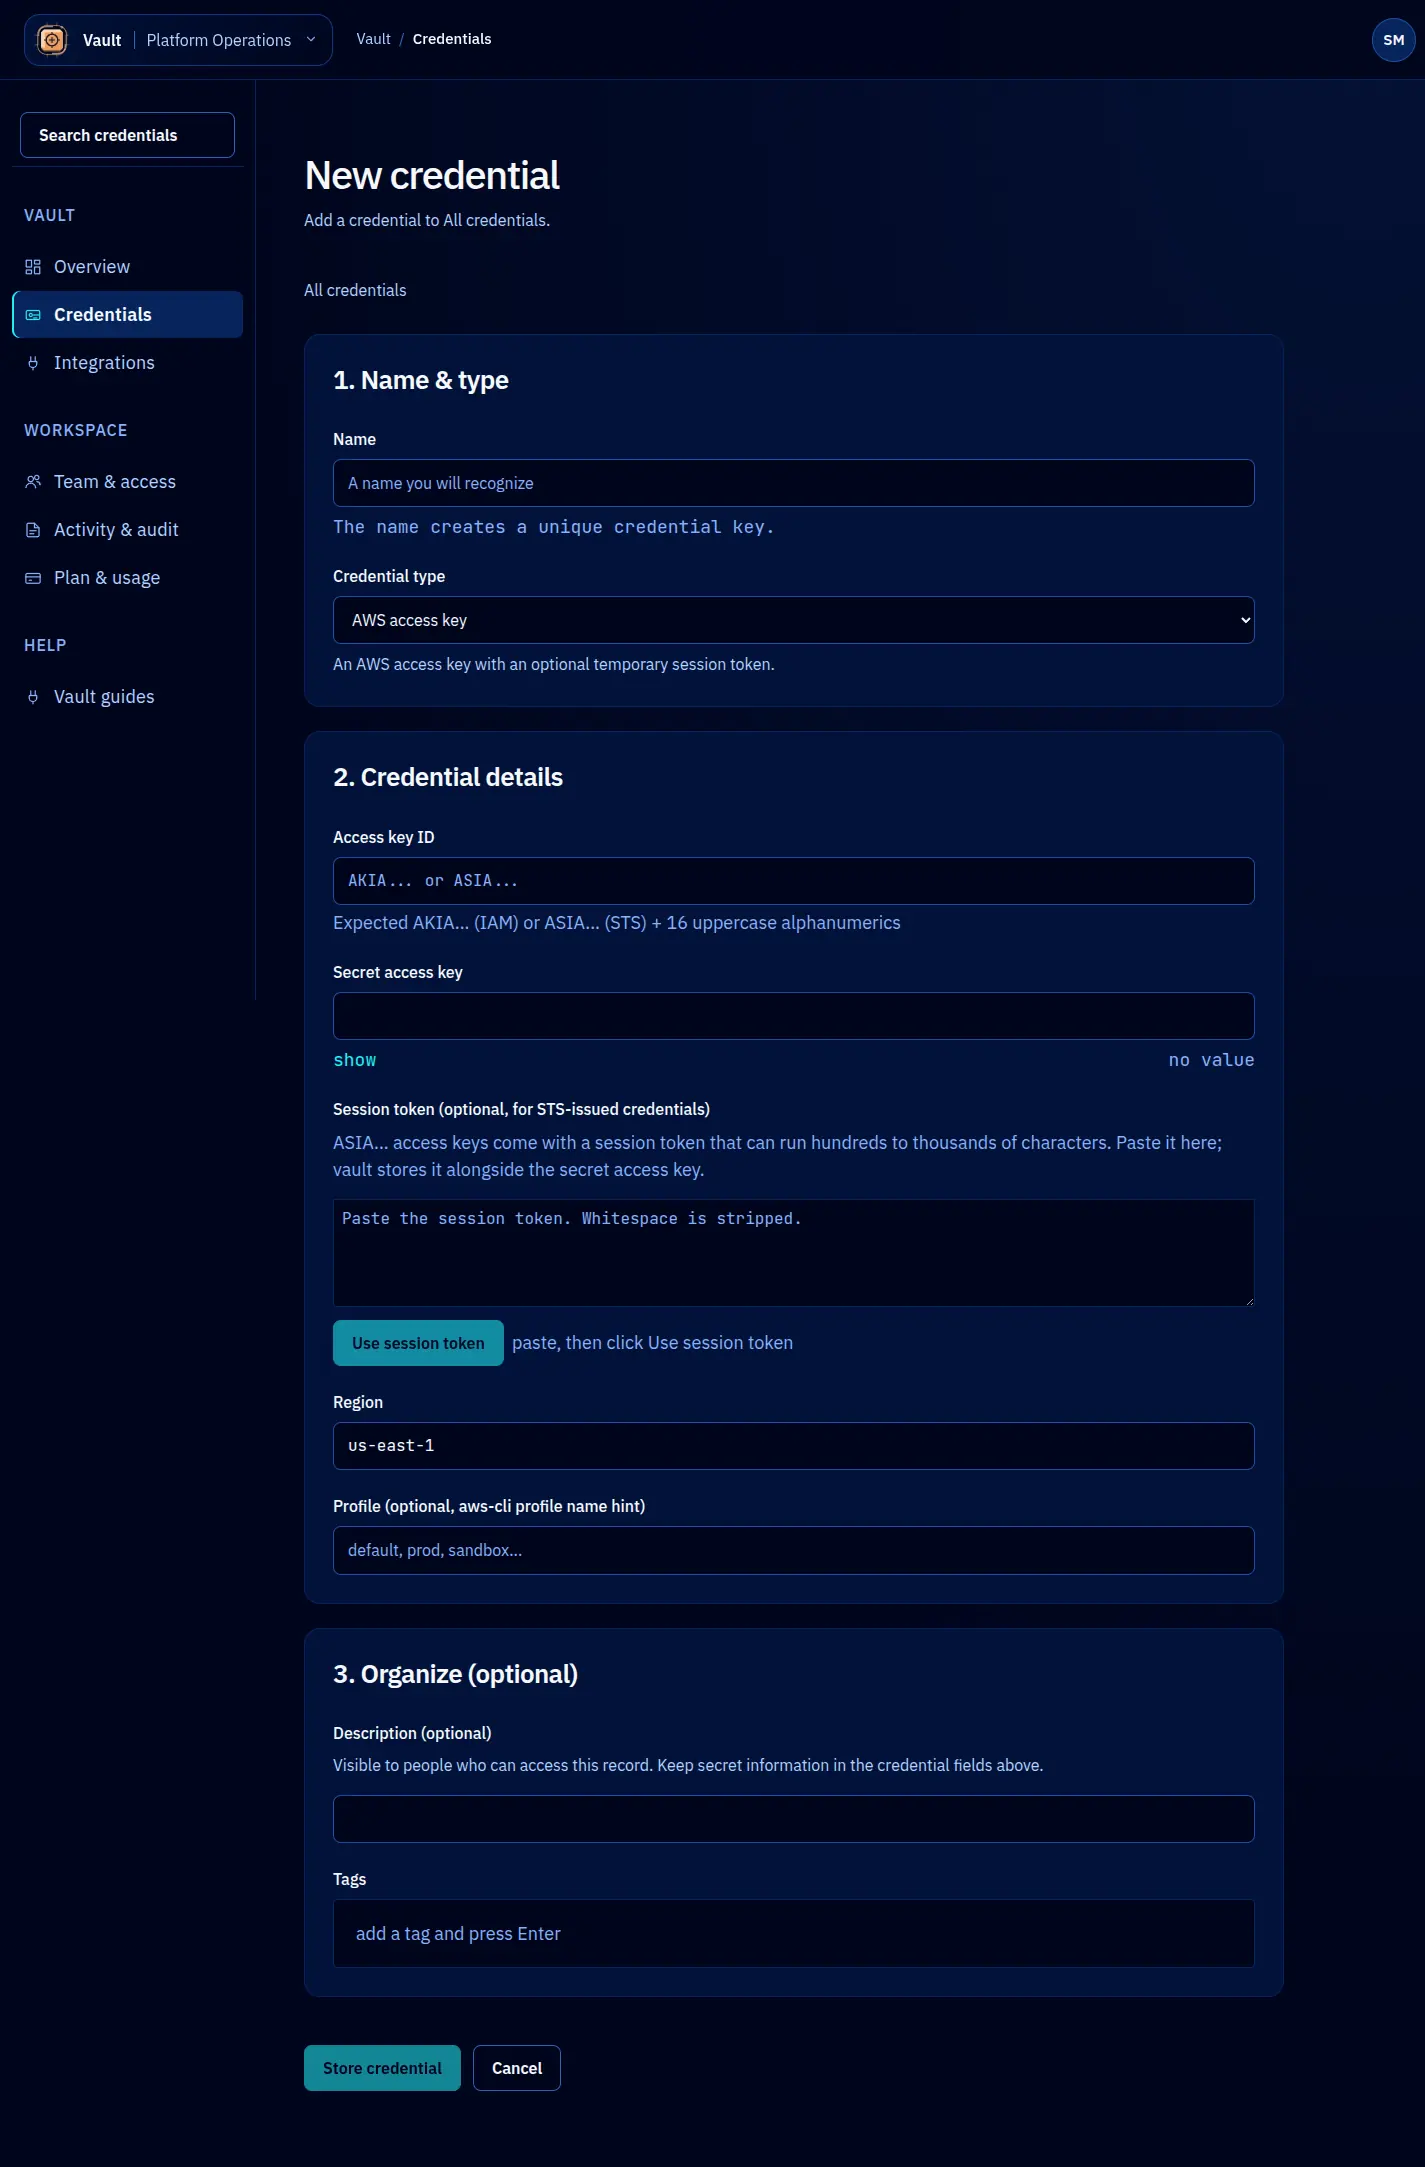
Use AWS access key when the record needs access key id, secret access key, region and optional session token or profile.
Create the record
- Open the intended folder and choose + New credential.
- Choose AWS access key from Credential type.
- Enter a recognizable name. Enter the issued key ID and secret, select the intended region and add the session token when using temporary credentials. Select Use session token to accept that intake, then store the full record.
- Review the storage location, description and tags. Do not place secrets in those metadata fields.
- Select Store credential. An intermediate Use action only accepts that field; it does not save the record.
- Open the saved record and check the name, type and available connection summary.
Validation messages stay with the form so you can correct the input. Switching types changes which fields are required. Recheck the selected type and location before submitting.
Retrieve or maintain it
Copy secret access key returns the primary value through the audited lease flow. For a complete structured record, use the TypeScript client or CLI. The key ID, region and session token are retrieved through the complete encrypted record. Vault does not renew STS credentials. Check their provider expiry before use.
Use the record’s Access tab for sharing, Activity for audit and leases, and Manage for rotation or archiving. A replacement requires the full typed record; existing secrets are not prefilled.
Screen reference