Navigation
Vault access. Public access is not open. This product is separate from initial Identity and Apparatus access.
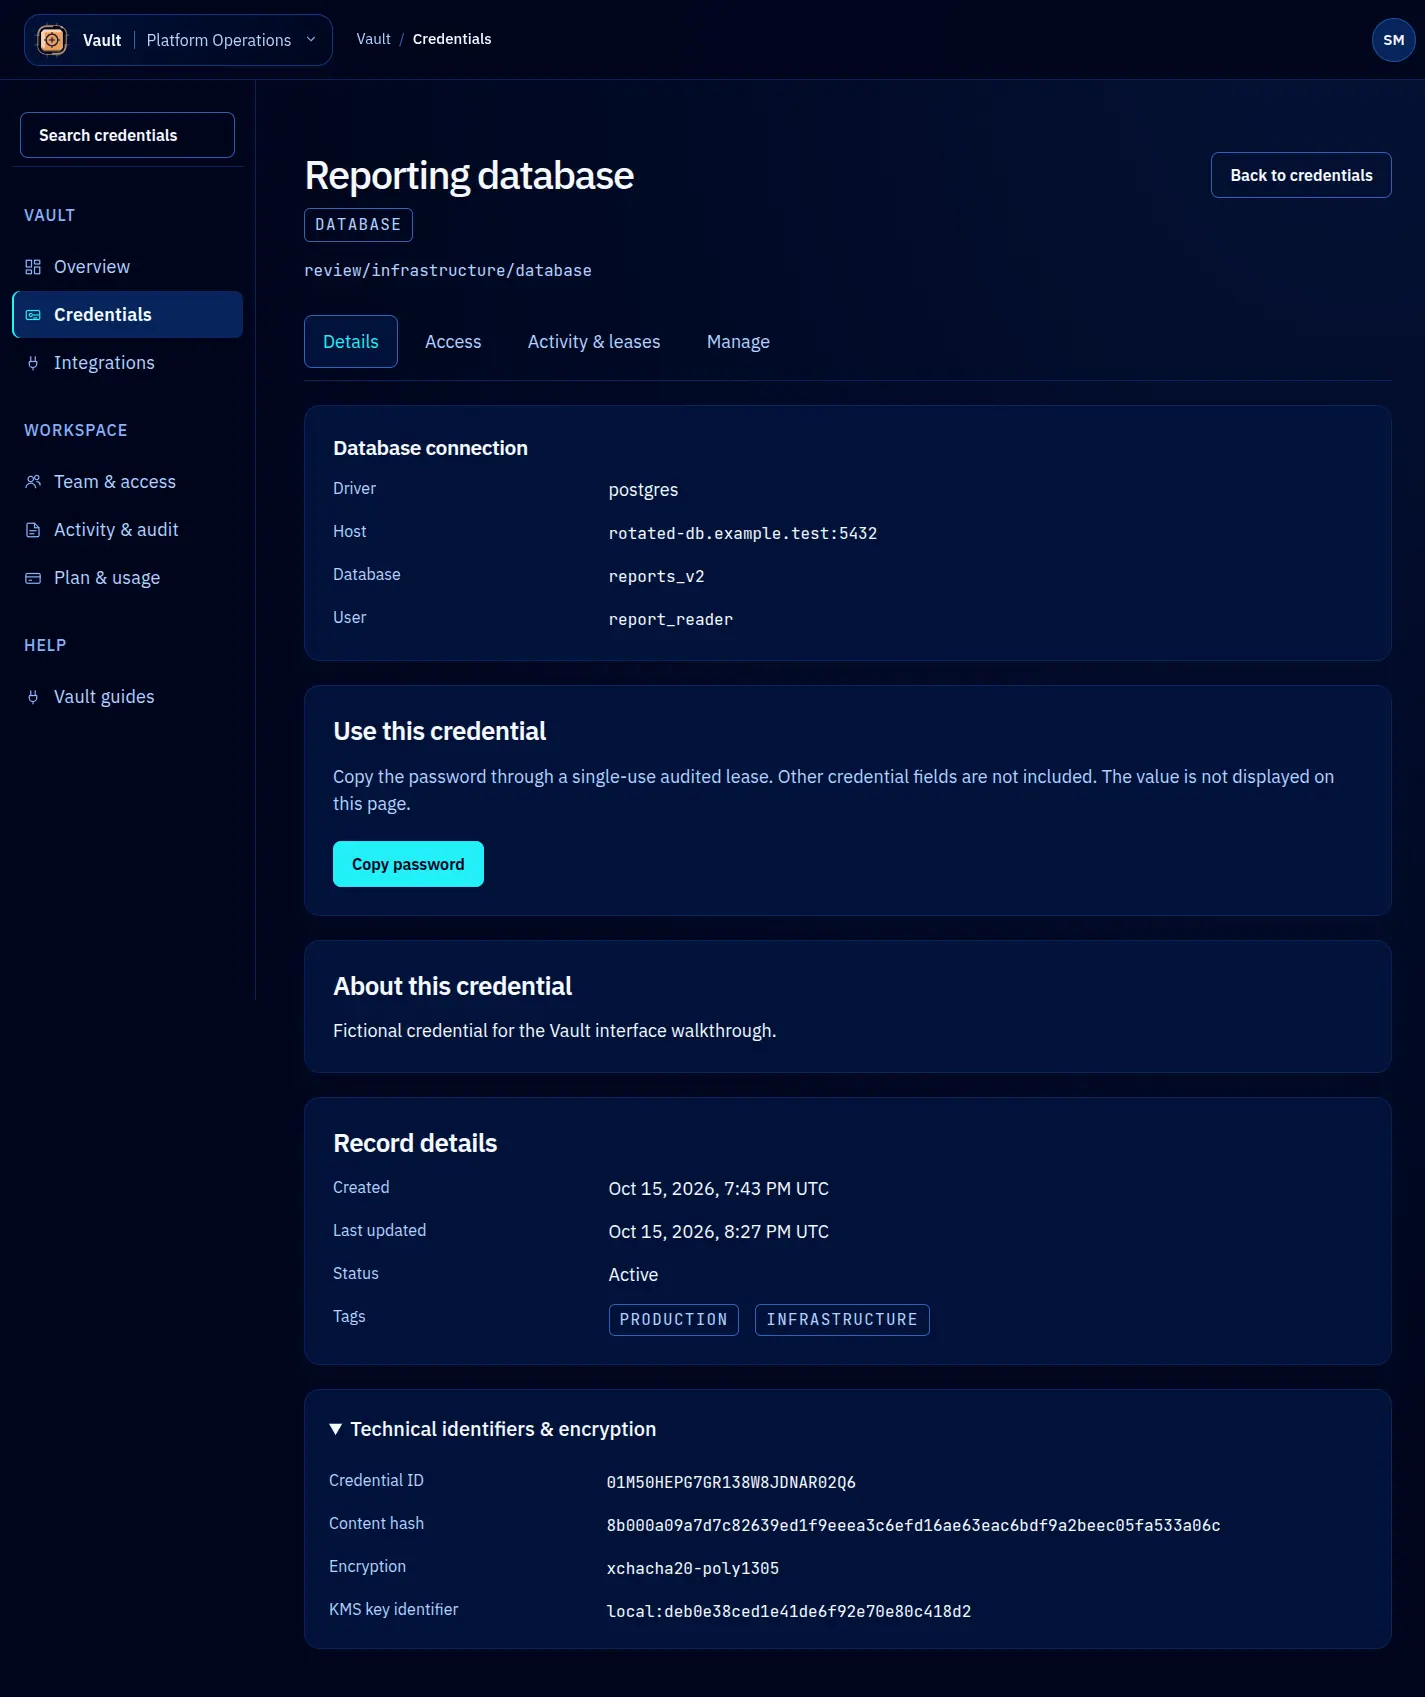
Screenshots use fictional demonstration accounts. Your data and available actions may differ. Reviewed October 16, 2026.
Concepts
Encryption Envelope
Current implementation
The reviewed Vault key providers use XChaCha20-Poly1305 authenticated encryption. Additional authenticated data binds encrypted values to tenant and credential context. Decryption rejects mismatched authenticated data or modified ciphertext.
Local provider
The local provider uses a configured 32-byte master key. Its security depends on protecting that key and the process using it. It does not establish a hardware security boundary or per-tenant key hierarchy.
Google Cloud KMS provider
The cloud provider generates a data encryption key for a credential, wraps that key through Google Cloud KMS, and encrypts the value locally. Key caching and rotation behavior depend on the provider configuration. Plaintext and unwrapped data keys exist in the trusted application process during use.
Limits
Encryption at rest does not prevent an authorized read from returning plaintext. It does not protect credentials after a consuming client exposes them in logs or model context. Claims about a deployed KMS, hardware protection or operational key rotation require deployment evidence.
See Security and Credential references.
Screen reference