Navigation
Vault access. Public access is not open. This product is separate from initial Identity and Apparatus access.
Screenshots use fictional demonstration accounts. Your data and available actions may differ. Reviewed October 16, 2026.
Clients
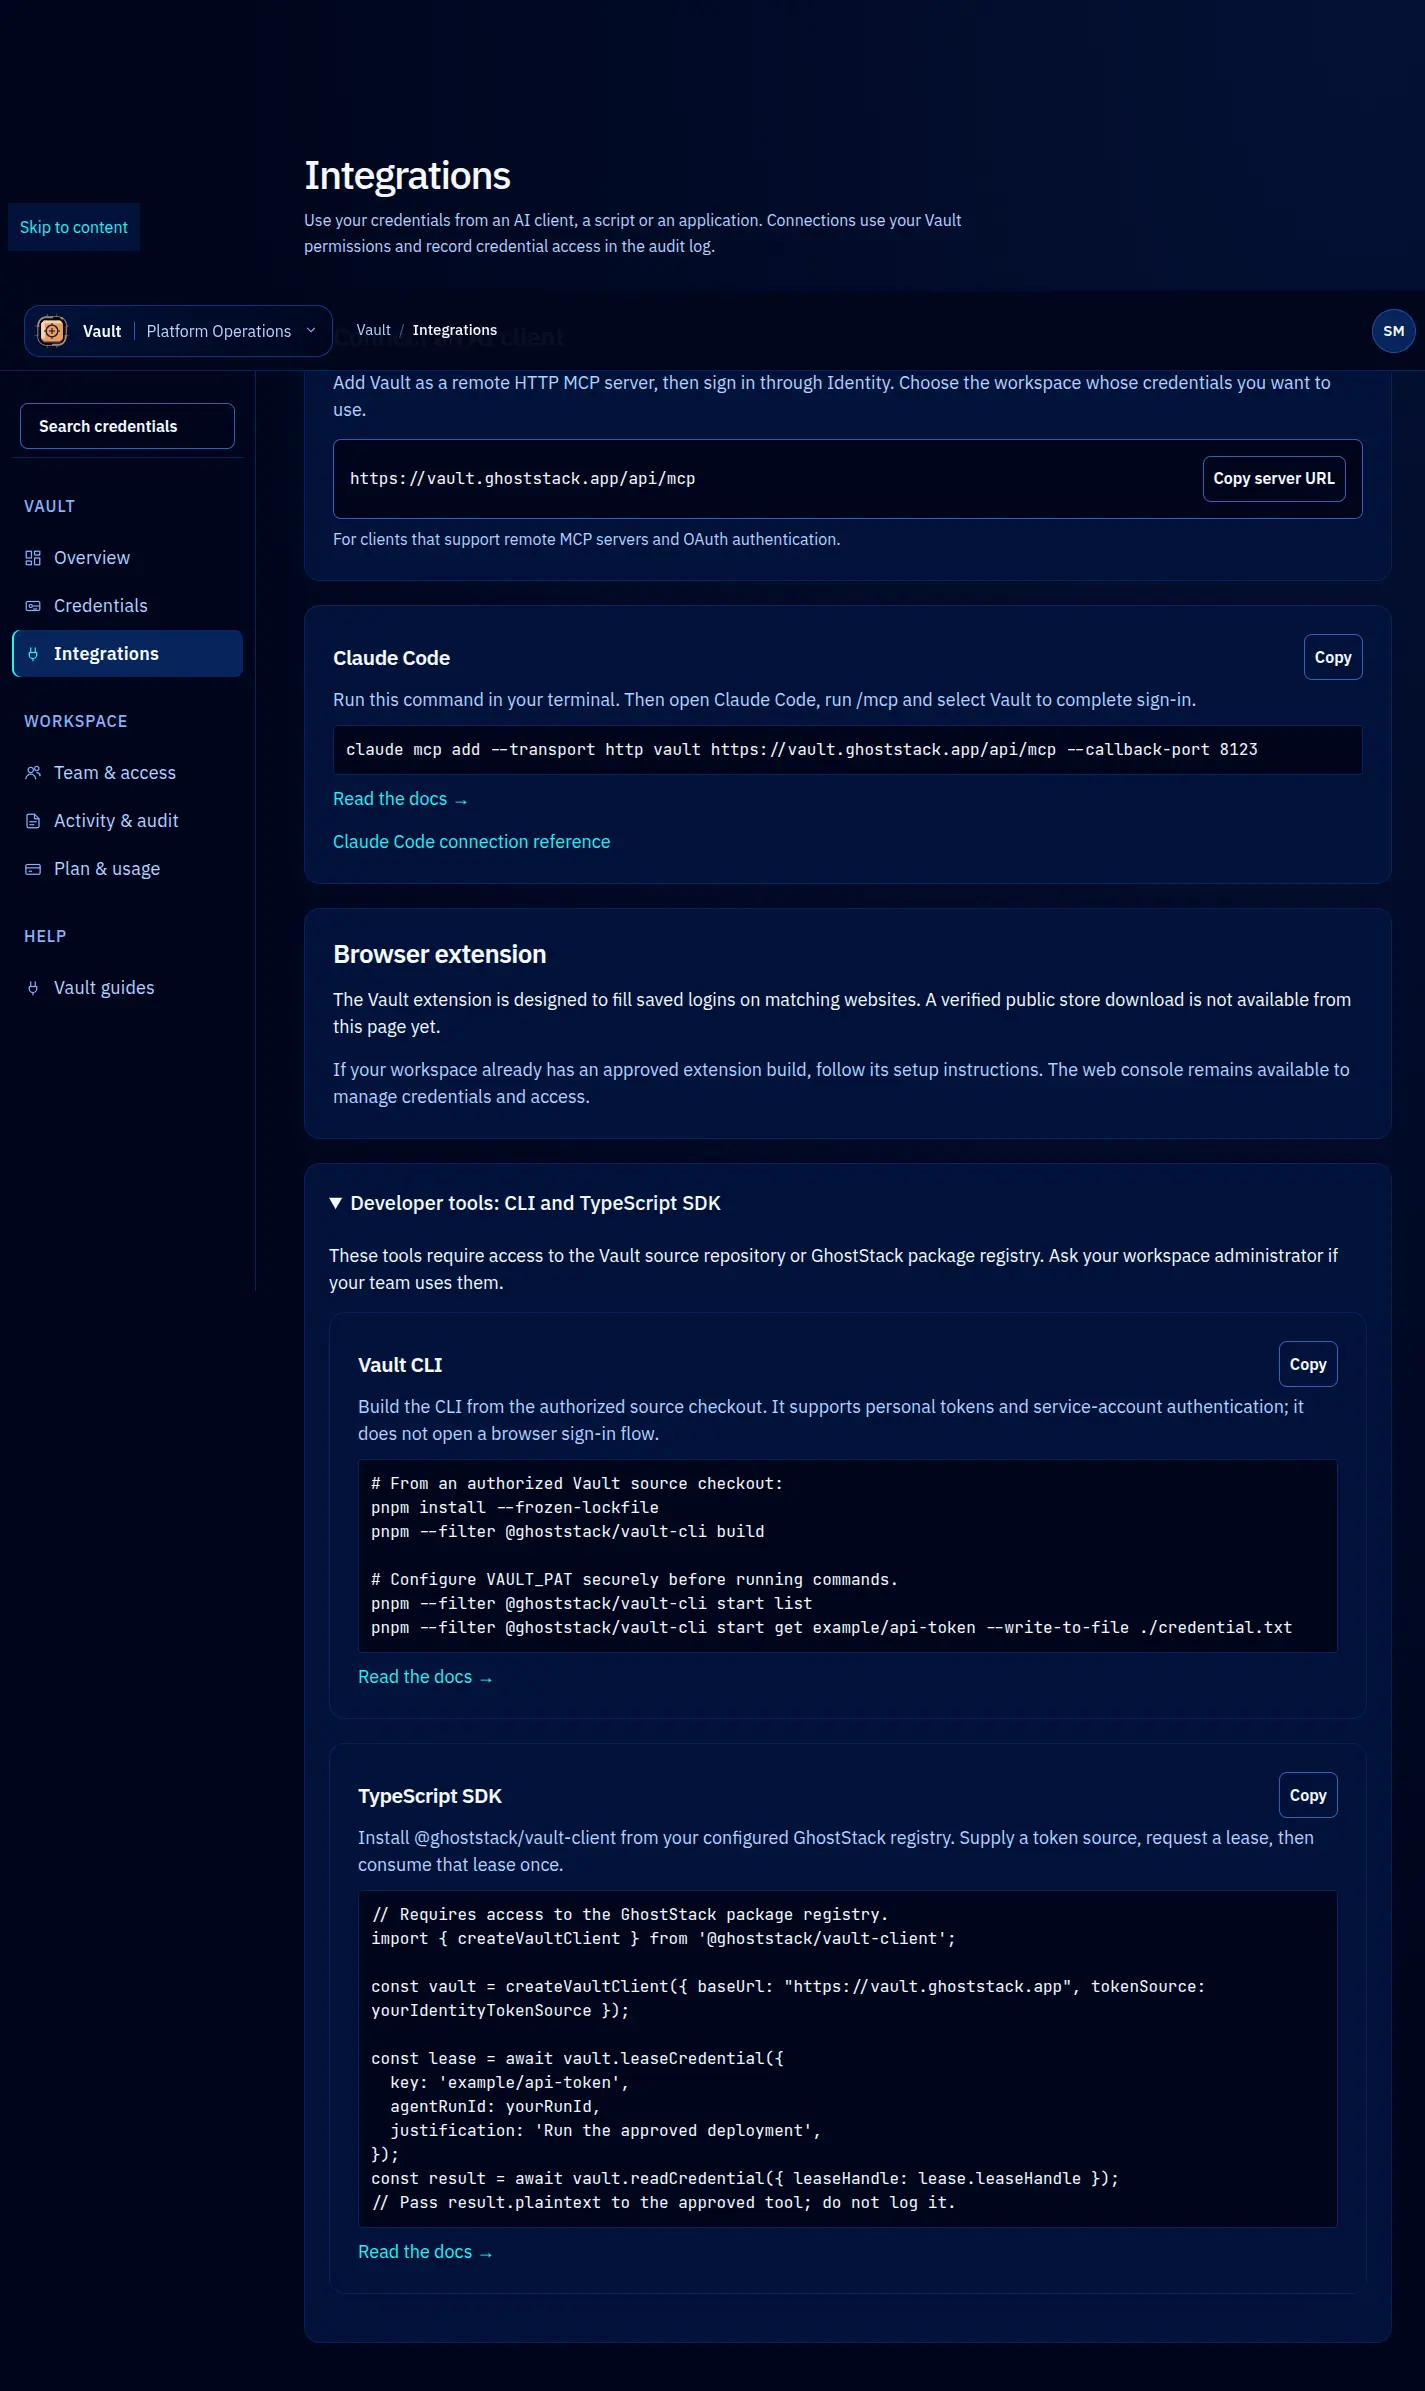
Start a TypeScript integration
Start with a server-side application that can securely obtain an Identity token. Do not put that token in a public browser bundle.
- Obtain authorized access to the private
@ghoststack/vault-clientpackage registry. - Have the operator confirm the REST audience and least required scope, workspace and record permission.
- Create a client with
createVaultClient({ baseUrl, tokenSource })as shown in the SDK guide. - Call
whoami()andlistCredentials()to check metadata before reading a secret. - Lease a fictional test credential with a run ID and justification, then redeem the returned handle once.
- Confirm that the application extracts the intended typed field without printing the response and that Vault records the event.
The older @ghoststack/vault-sdk and Vault.connect() examples do not describe the current client. Use the current method reference. No code sample in this documentation supplies credentials or authorizes a real production read.
Screen reference