Navigation
Vault access. Public access is not open. This product is separate from initial Identity and Apparatus access.
Screenshots use fictional demonstration accounts. Your data and available actions may differ. Reviewed October 16, 2026.
Access and maintenance
Share credentials and folders
Workspace membership is managed by Identity. Vault roles and record grants determine what a member can do with credentials. Start with the person’s existing workspace membership; a grant is not an invitation.
Share one credential
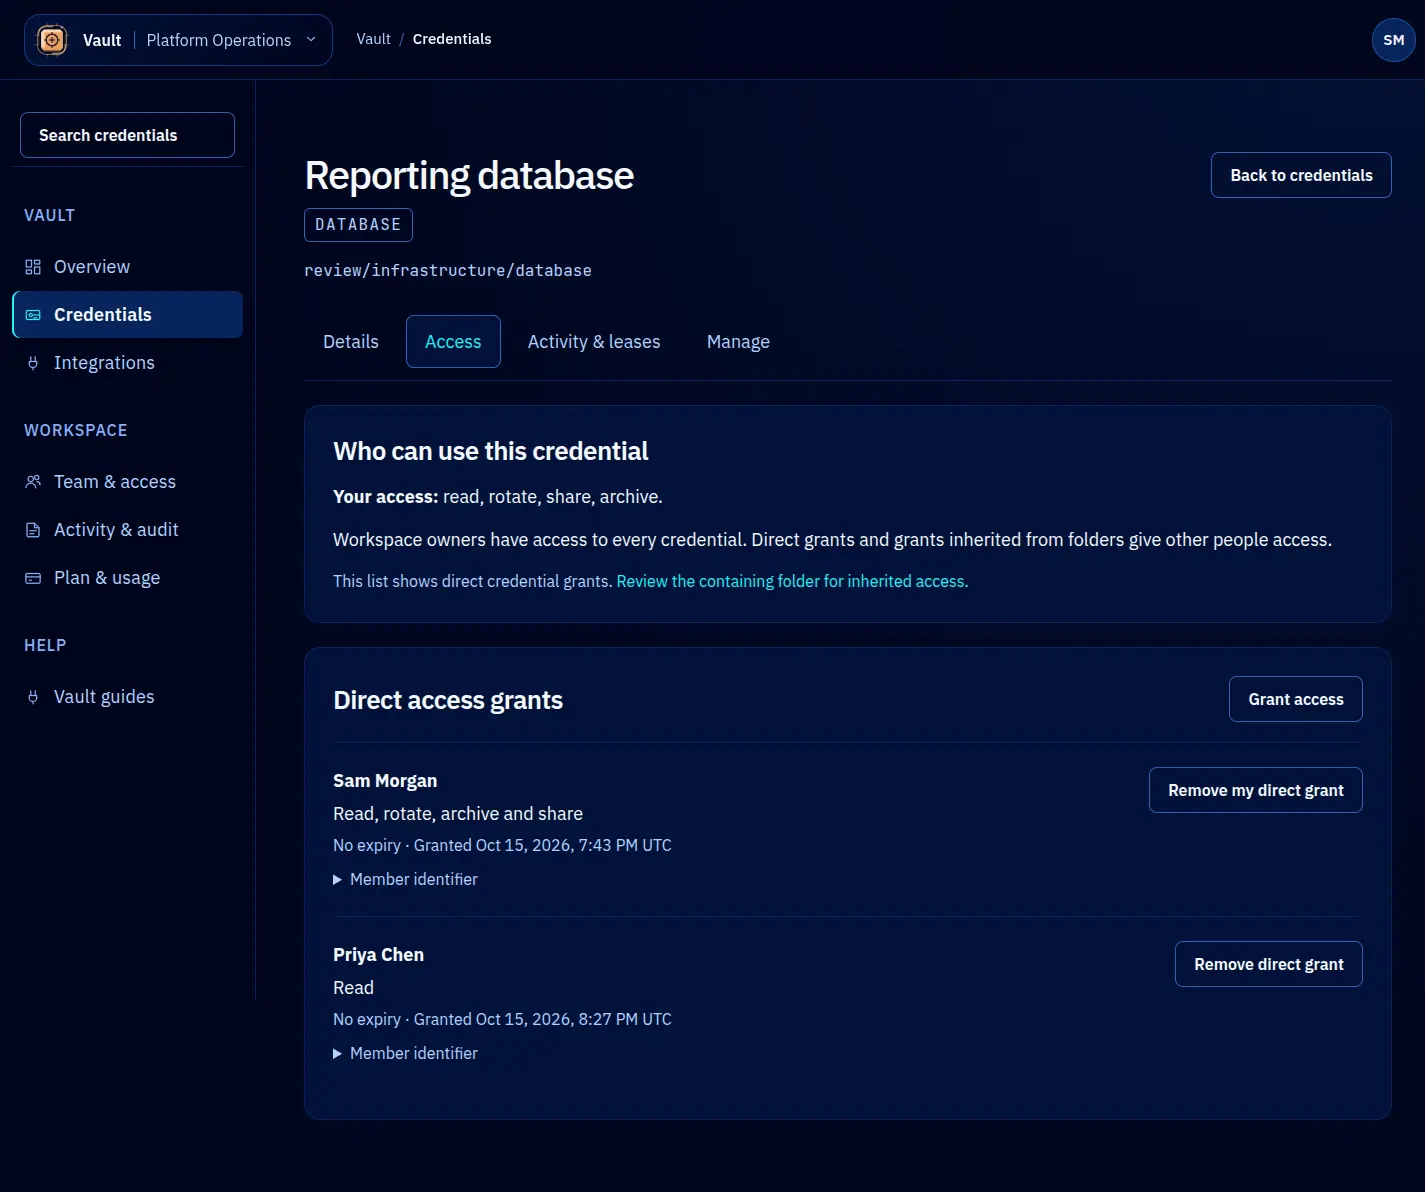
- Open the credential and select Access.
- Check Your access and the existing grants.
- Select Grant access, choose the intended workspace member, and select the appropriate permission. Read-only is the initial choice.
- Set an expiry when the access is temporary, then save the grant.
- Ask the member to check the record in the correct workspace.
Share a folder
Open the folder, expand Folder access, and select Grant folder access. Descendant records inherit applicable folder grants. Review the full subtree before granting access to a broad parent. The panel distinguishes direct, inherited and older prefix grants; a service-account grant is not a human member.
Remove access carefully
Use Remove direct grant to revoke that specific grant. An inherited grant, another matching grant or owner privilege can still provide access. Follow the containing-folder link to find the source. Downgrading a role or revoking a grant should change the person’s subsequent authorized requests.
Revocation cannot erase a secret already copied or used. If someone must stop using an underlying credential, revoke or rotate it at the provider as well. See rotation.
Screen reference